

/api/* (except explicitly exempt paths) must include a Bearer token.
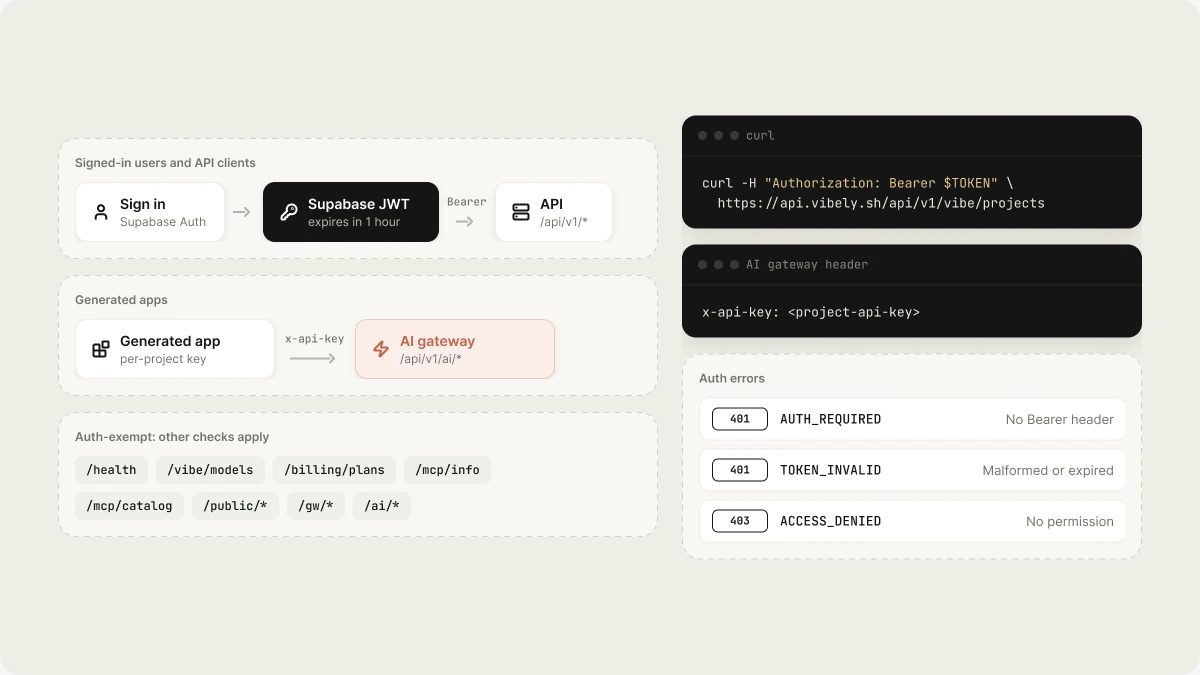
Getting a token
Vibely is a single-page app — auth happens client-side via Supabase Auth. The frontend manages token acquisition and refresh transparently through@supabase/ssr.
For API consumers (MCP clients, CI scripts, external services):
- Sign in to Vibely at
https://vibely.sh - The session token is stored in the browser
- For programmatic access, use an MCP API key (see below)
Bearer token
Token lifecycle
- Tokens are short-lived (1 hour by default)
- The frontend client refreshes automatically on 401
- If calling the API directly, handle 401 by re-authenticating
Auth-exempt paths
These paths skip Bearer validation — each authenticates itself by some other means (its own signature check, anx-api-key, or a provider callback secret):
GET /api/v1/health,GET /api/v1/vibe/models,GET /api/v1/vibe/providersGET /api/v1/billing/plans,GET /api/v1/billing/config,POST /api/v1/billing/webhookPOST /api/v1/git/oauth/callback,/api/v1/supabase/oauth/callback,/api/v1/stripe/oauth/callback/api/v1/mcp/info,/api/v1/mcp/catalog,/api/v1/mcp/oauth/begin,/api/v1/mcp/oauth/callback/api/v1/ai/*— the AI gateway, which does its ownx-api-keycheckPOST /api/v1/internal/analytics/collectand the other/api/v1/internal/*webhooks/api/v1/public/*and/api/v1/gw/*
isAuthExempt() in
src/middleware/auth-exempt.ts. Matching is exact or by an anchored pattern —
never a loose substring, so a path that merely contains an exempt one
(.../files/git/oauth/callback) still authenticates.
AI gateway API keys
The/api/v1/ai/* gateway — what a generated app calls for chat, images, video,
speech, and embeddings — authenticates with a per-project API key instead of a
user JWT:
401 x-api-key header is required before any model call is made.
Error responses
See Error Format for the full response shape.